Architecting Stable Identity Mapping for Messaging Integrations
Relying on mutable identifiers like usernames or phone numbers for database keys leads to data fragmentation; developers must prioritize immutable numeric identifiers for long-term state management.
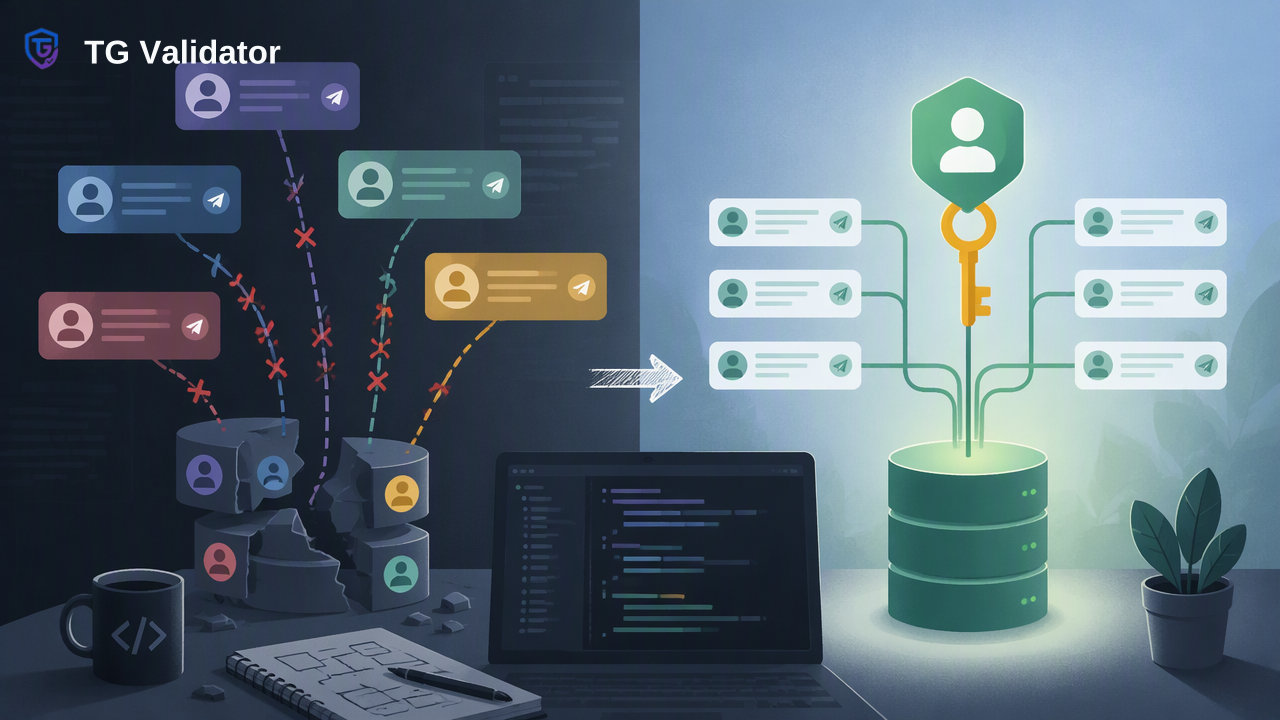
In distributed systems, the choice of a primary key for user entities is often treated as a trivial implementation detail. However, when building messaging integrations—where external identifiers like usernames or phone numbers are frequently exposed—this choice becomes a critical architectural decision. Relying on mutable identifiers as database keys creates a fragile foundation that inevitably leads to data fragmentation, orphaned records, and complex migration debt.
The Problem: The Illusion of Stability
When a developer begins building a notification service, the most intuitive approach is to use the user’s handle or phone number as the primary identifier in the database. It is human-readable, readily available from the client, and simplifies initial queries.
However, in the context of messaging platforms, these identifiers are inherently mutable. A user may change their handle, or a phone number may be reassigned to a new subscriber. When the database uses these values as foreign keys to link message threads, CRM entries, or notification logs, the system becomes tightly coupled to the user's external state.
If a user updates their handle, the application must either perform a cascading update across all related tables—which is computationally expensive and prone to locking issues—or accept that the historical data is now disconnected from the current user profile. This leads to "identity drift," where the system loses the ability to reconstruct a coherent history for a single entity.
The Architectural Decision: Immutable Surrogate Keys
To ensure long-term stability, the architecture must decouple the internal identity from the external identifier. The recommended approach is to implement an immutable, system-generated numeric identifier (a surrogate key) as the primary key for all user-related records.
The Strategy
- Internal Identity: Assign a unique, immutable ID (e.g., a UUID or a monotonically increasing integer) to every user upon creation.
- Mapping Layer: Maintain a separate mapping table that links the immutable internal ID to the current external identifier (e.g., username or E.164 phone number).
- Referential Integrity: All foreign keys in the CRM, messaging, and notification tables must point to the internal ID, never the external handle.
Trade-offs and Constraints
This approach introduces a slight increase in query complexity. Retrieving a user's record by their handle now requires a join or a lookup in the mapping table. However, this is a necessary trade-off. The cost of an additional index lookup is negligible compared to the operational overhead of repairing broken data relationships caused by identifier changes.
Furthermore, this architecture adheres to the principle of data minimization. By isolating external identifiers in a specific mapping table, you limit the surface area of sensitive data. If an external identifier needs to be updated or purged, the change is localized to the mapping table, leaving the core business logic and relational integrity of the message history untouched.
Counterexample: The "Handle-as-Key" Failure
Consider a hypothetical scenario where a notification service uses a username as the primary key for a message_threads table.
- The Incident: User "Alpha" has a thread history stored under the key
alpha. - The Change: User "Alpha" changes their handle to "Beta."
- The Result: The application updates the user profile but fails to update the
message_threadstable. New messages sent to "Beta" create a new thread, while the old messages remain orphaned under the now-defunctalphakey.
The system now has two distinct threads for the same user, and the CRM shows a fragmented view of the user's engagement. If the system had used an internal ID (e.g., user_101), the message_threads table would have remained perfectly intact regardless of the handle change.
Operational Risks and Validation
The primary risk of this architecture is the management of the mapping table. If the mapping table is lost or corrupted, the link between the internal state and the external identity is severed. Therefore, the mapping table must be treated with the same high-availability standards as the core user database.
Evidence that would invalidate this decision: This architectural choice would be invalidated if the system requirements shifted to a model where external identifiers are strictly guaranteed to be immutable by the upstream provider. If a platform were to provide a permanent, immutable global ID for every user that is guaranteed never to change, the need for a local mapping table would be reduced, as the platform's ID could serve as the primary key.
However, in most messaging integrations, external identifiers are subject to platform-level changes. Relying on an external provider's ID as your primary key is also a form of vendor lock-in; if you ever migrate to a different messaging provider, you would face the same fragmentation issues all over again.
Implementation Considerations
When integrating with external services, such as those that provide registration status or profile information, ensure that your internal system handles the asynchronous nature of these checks correctly.
For instance, when performing bulk checks on phone numbers or usernames, the results—which may include internal platform IDs or activity signals—should be mapped to your internal surrogate keys. If a bulk task returns a status for a phone number, the application should look up the internal ID associated with that number and update the relevant records.
When using APIs for these checks, be mindful of the documented concurrency and timeout behaviors. For example, when performing a single check or a multi-check, ensure your application logic respects the documented timeout limits. If a check takes longer than the allowed duration, the application should handle the failure gracefully rather than assuming a result.
Similarly, when using asynchronous bulk tasks, do not attempt to poll for results more frequently than the recommended interval (e.g., once every 30 seconds). This ensures that your integration remains stable and respects the operational constraints of the service provider.
Conclusion
Architecting for stable identity mapping is an exercise in defensive engineering. By prioritizing immutable numeric identifiers, you insulate your application from the volatility of external platforms. While it requires more upfront design effort and a more robust database schema, the result is a system that maintains data integrity over time, simplifies maintenance, and provides a consistent experience for the end user, regardless of how often they change their public-facing handle.
About the author
- https://tgvalidator.com Check if a phone number is registered on Telegram. Verify a single number instantly.
Comments
Join the discussionNo comments yet. Be the first to comment.